Information may be obtained or stored in your browser by cookies when you access the Website. This information is related to the user, the user settings or device. It is primarily used to ensure the site functions as expected by the user. We respect your right to privacy. Therefore, you can select to not allow some types of cookie. Please click on the different category headings to check the details and then change our default settings.
Strictly Necessary Cookies are cookies that are essential for this site to function properly. Strictly Necessary Cookies do not store information that can identify individuals. Strictly Necessary Cookies are used to view this site. Therefore, you cannot refuse the use of Strictly Necessary Cookies from these cookie settings. However, you can refuse the use of Strictly Necessary Cookies from the settings of your browser at any time. Please note that parts of the site may not function if you refuse the use of Strictly Necessary Cookies.
This site uses the following Strictly Necessary Cookies.
Cookie name: gdprCookieEn
Cookie name: optGA
Cookie name: optPardot
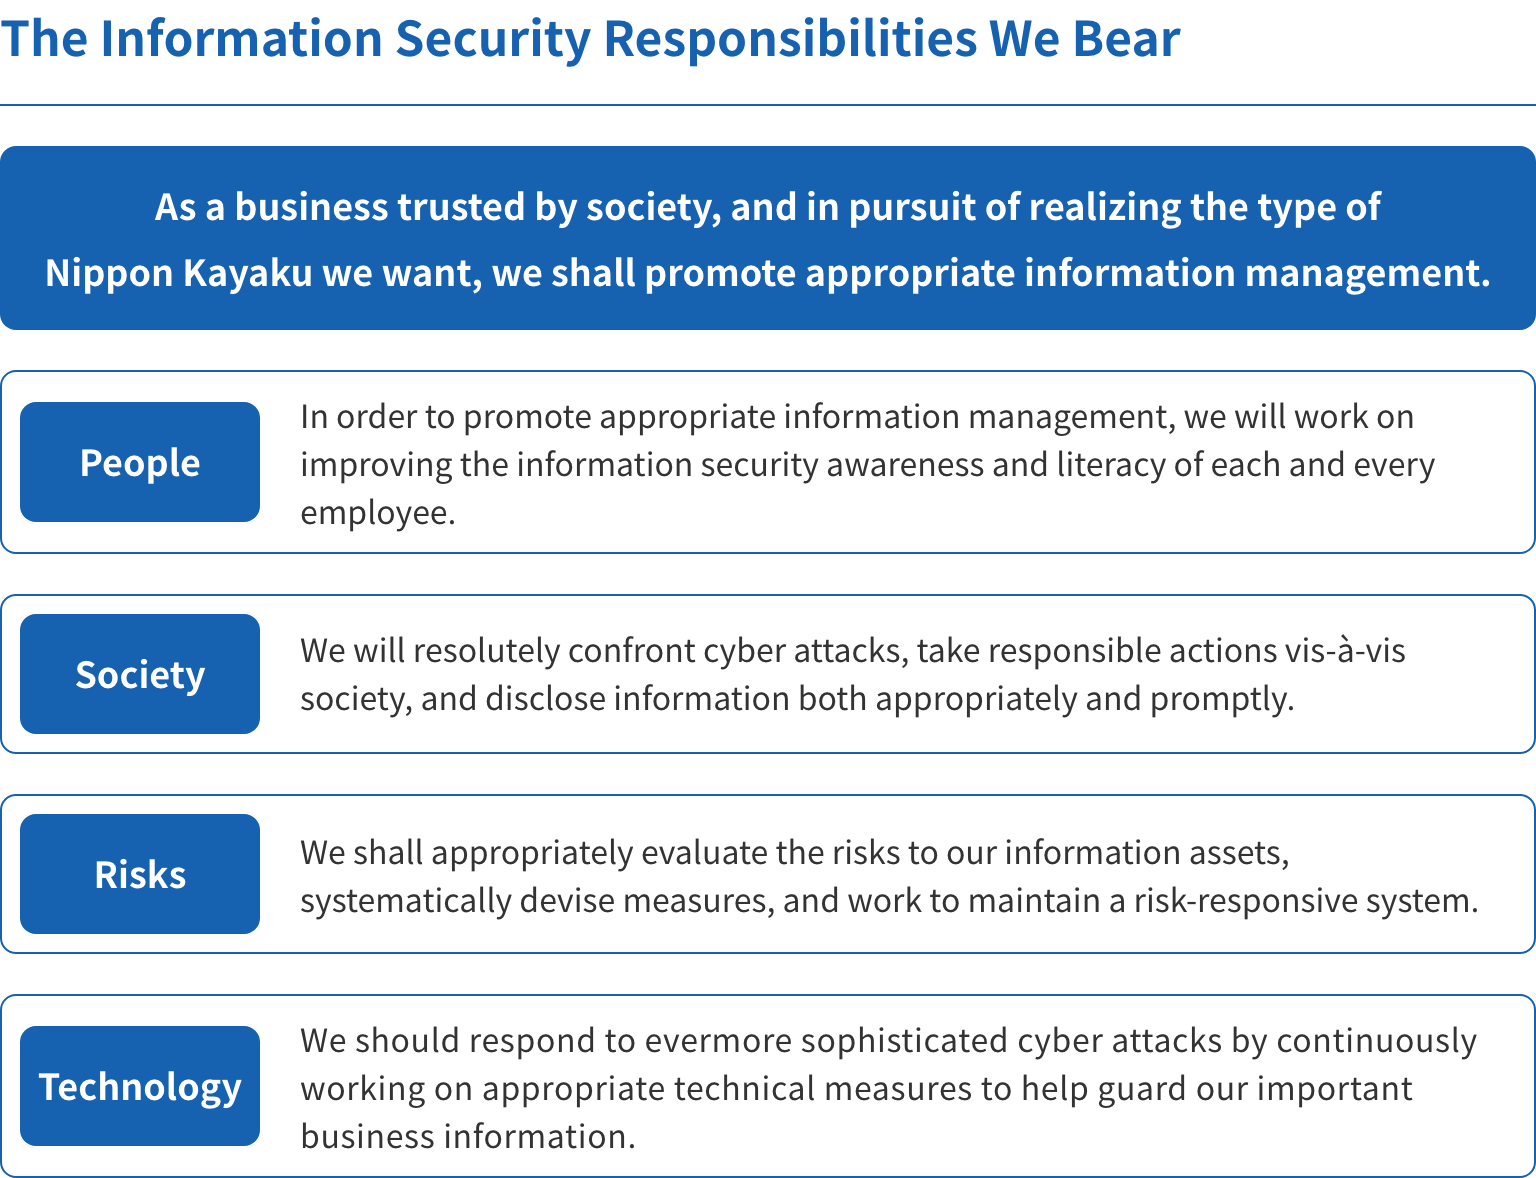
The Nippon Kayaku Group is promoting Digital Transformation (DX) to improve operational efficiency and productivity and to support diverse working styles. However, cyberattacks and unauthorized access are becoming increasingly frequent, sophisticated, and advanced, resulting in growing cyber risks. We regard the risks to business continuity arising from information leakage and computer system disruptions as key management challenges. To earn and maintain the trust of society as a whole, including our customers, business partners, investors, employees, and other stakeholders, we have established the Nippon Kayaku Group Information Security Policy and The Information Security Responsibilities We Bear*, based on the Nippon Kayaku Group Charter of Conduct and Code of Conduct. We continuously incorporate information security into our day-to-day operations to protect corporate information and improve information security awareness and literacy.
The Nippon Kayaku Group recognizes the information it possesses in the conduct of corporate activities as a key management resource, views information security initiatives as a key management issue, and has determined the following policy approach towards maintaining and improving a system capable of safeguarding its information assets appropriately, continually and across the organization.
The Nippon Kayaku Group shall appropriately protect its information assets from threats to their value (in terms of confidentiality, integrity and availability).
The Nippon Kayaku Group shall observe the laws and policies determined by each country, contractual obligations and other social norms when sharing necessary information in the conduct of business and effectively utilizing such information.
The Nippon Kayaku Group shall, in line with the stipulations of its Charter of Conduct and Code of Conduct, both prepare and uphold regulations and standards concerned with the management of the information assets in its possession.
The Nippon Kayaku Group shall, in order to protect and appropriately manage all information assets in its possession, formulate a system which bears necessary responsibility for information security, and deploy, to each group company and organization, information security managers and security-specialist personnel with the relevant expertise and technical knowledge.
The Nippon Kayaku Group shall view its policy approach to information security as part of its overall management approach, and ensure the necessary staff and budgets are suitably allocated for technical and physical measures.
The Nippon Kayaku Group shall visualize and assess the hypothetical risks of information leakage and business suspension due to cyberattacks, and continually implement relevant measures which extend to the supply chain.
The Nippon Kayaku Group shall, in instances of critical information asset incidents, respond promptly to minimize the damage caused, and, based on root cause analyses, formulate recurrence prevention measures.
The Nippon Kayaku Group shall, with respect to every related party in its employ, promote increased information security literacy by periodically and continuously delivering education and training scenarios based on critical information asset incidents.
The Nippon Kayaku Group shall periodically assess and review this policy as it continually enacts information security initiatives.
Jun 26th 2025
Member of the Board Managing Director
Chair of the Information Risk Management Subcommittee

To minimize information security risks, which are a key element of crisis management, and to maintain an appropriate level of security, continuously review countermeasures in response to changing circumstances, and oversee company-wide implementation and awareness, we have established the Information Risk Management Subcommittee.
This subcommittee meets, in principle, twice a year, and additionally as necessary. It is chaired by the Officer in charge of Information Systems, and comprises representatives of every business unit’s planning department plus representatives from general administrative departments unattached to any particular business unit. It also coordinates with the Corporate Information Officer, Person in-charge of Corporate Information, and System Administrator assigned to each company division and workplace.
Important matters discussed by the Subcommittee are reported to the Sustainable Management Meeting and the Board of Directors, which provide feedback as appropriate.
Furthermore, to deal with security incidents that could cause significant damage to the Company’s management or business operations, materially affect its relationships with affiliated companies, business partners, and other customers, or result in a loss of trust, such as cyberattacks and unauthorized access to confidential information, we activate a Computer Security Incident Response Team (CSIRT) to centrally coordinate the response under the leadership of the Information Risk Management Subcommittee Chair. Depending on the anticipated severity of the impact, the President or the Chair of the Risk Management Committee may serve as the CSIRT Leader. The CSIRT works promptly to limit the spread of damage. Once containment has been completed, it focuses on recovery and measures to prevent recurrence.
Scroll horizontally to view more.
| FY2025 Targets | FY2025 Results |
|---|---|
| Develop a BCP manual and conduct a cyberattack response exercise in accordance with the Detailed Rules for the Information Risk Management Regulations. | A cybersecurity incident response exercise was conducted in accordance with the Detailed Rules for the Information Risk Management Regulations (CSIRT Manual). |
| FY2026 Targets |
|---|
| Through further enhancement and expansion of information security policies, rules, and standards, ensure compliance with the requirements of the “Supply Chain Security Assessment System ” laid down by Japan’s Ministry of Economy, Trade and Industry (METI) |
Scroll horizontally to view more.
| Classification of measures | Details |
|---|---|
| (1) Organizational Measures |
|
| (2) Human and Legal Measures |
|
| (3) Physical Measures |
|
| (4) Technical Measures |
|
The Nippon Kayaku Group communicates its information security rules to all executives, employees, including contract and part-time employees, and temporary staff, and regularly provides information security training and phishing email response exercises.
| Training Program | Main Contents | Target Audience | FY | Delivery style | Frequency |
|---|---|---|---|---|---|
| Executive Cybersecurity Training |
|
Executives | 2025 | Seminar | 1 |
| Information Security Awareness Training |
|
Executives, employees, and external parties using company IT tools | 2025 | e-Learning, distribution of materials, group training | 1 |
| Phishing Email Awareness Training |
|
Executives, employees, and external parties using company IT tools | 2025 | e-Learning | 1 |
| Phishing Email Simulation Exercise |
|
Executives, employees, and external parties using company IT tools | 2025 | Exercise | 4 |
| Cybersecurity Incident Response Exercise |
|
CSIRT and Information Risk Management Subcommittee members | 2025 | Exercise | 1 |
The number of major information security incidents that occurred within the Nippon Kayaku Group over the past three years is shown below.
Scroll horizontally to view more.
| Indicators | Scope | Unit | 2021 | 2022 | 2023 | 2024 | 2025 |
|---|---|---|---|---|---|---|---|
| Number of Major Information Security Incidents * | consolidated | cases | - | - | 0 | 0 | 0 |
The Nippon Kayaku Group recognizes the importance of personal information and complies with the Act on the Protection of Personal Information and other applicable laws and regulations concerning the personal information it handles. We consider the protection of personal information to be a social responsibility and are committed to ensuring its proper management and protection.
We have also established our Personal Information Protection Policy for external stakeholders, with purposes of use, security control measures and contact details for consultations and complaints all published on our website so that the information is readily accessible to the public.
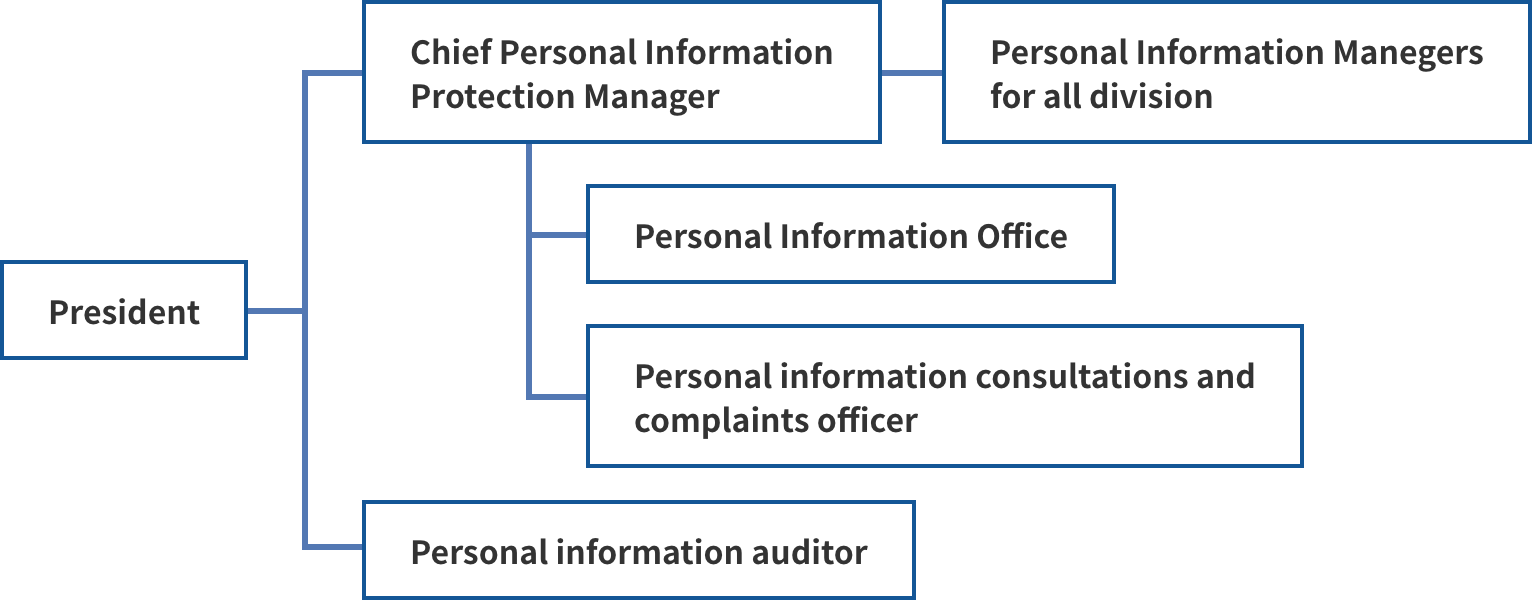
We have established the Personal Information Management Regulations and, under the supervision of the Chief Personal Information Protection Officer, appointed Personal Information Managers in each department. Personal information handled in the workplace is classified according to its level of importance on an ongoing basis and registered in a management database.
We also provide training to all personnel three times a year, conduct an annual inventory of personal information, and perform an annual audit. Through these activities, we raise awareness of personal information protection and enhance the effectiveness of our protection measures.

| Training Program | Main Content | Target Audience | FY | Delivery Method | Frequency | Completion Rate |
|---|---|---|---|---|---|---|
| Legal training |
|
Executives, employees (including contract and part-time employees), and temporary staff | 2025 | e-Learning, Group Training | 3 | Ave: 84.8% |
In the event of a personal information breach, we will respond in accordance with our Information Leakage Incident Response Procedures.
As of March 31, 2026, no personal information breach incidents had occurred.